
What You’ll Learn
- How MainWP secures the initial site connection
- How MainWP requires at least one initial connection authentication method
- How HTTPS encrypts Dashboard-to-Child traffic
- How request authentication prevents unauthorized access
Initial Connection Security
MainWP 5.3 introduced enhanced security features for the site connection process.MainWP Child requires at least one initial connection authentication method: Password Authentication, Unique Security ID, or both. You cannot disable both methods in MainWP Child settings.
Password Authentication
MainWP uses the WordPress administrator’s password for verification during initial setup. This feature is enabled by default and ensures only verified administrators can authorize connections. It can be disabled only when Unique Security ID remains enabled.Unique Security ID
Unique Security ID can be used as an alternative or additional authentication check during setup. When enabled, this ID must match on both Dashboard and Child Site for the connection to succeed. It is optional only when Password Authentication remains enabled. If Password Authentication is disabled, Unique Security ID is required.Connection Timeout
The MainWP Child plugin includes a connection timeout to minimize exposure. After activation, if no connection is established within the specified time (in minutes), the plugin automatically deactivates itself. This prevents idle plugins from remaining accessible. Set the limit in Set Connection Timeout at WordPress Admin > Settings > MainWP Child > Settings. The default is 20 minutes. Enter0 to turn off the timeout.
While the site is not connected, the MainWP Child activation notice in WordPress Admin shows:
- Site URL and Administrator username fields with Copy buttons, so you can paste them into the Dashboard’s Add Site form
- A live countdown of the minutes left before MainWP Child deactivates itself
The countdown is not shown when the timeout is turned off or when MainWP Child is loaded as a must-use plugin, because the plugin does not deactivate itself in those cases.
Disconnect Site Option
The Disconnect Site feature allows you to clear all connection data for a Child Site directly from the Dashboard. Use this when:- Decommissioning sites
- Re-establishing secure connections
- Troubleshooting setup issues
Post-Connection Security
After a site is added, MainWP Dashboard signs requests with that site’s private key. MainWP Child verifies the signatures using the public key saved during connection.Key Pair Generation
With the default OpenSSL connection method, MainWP Dashboard creates a key pair when it first connects to a child site:- MainWP Dashboard generates a 2048-bit RSA public/private key pair using
openssl_pkey_new() - Public key is saved on both the child site and Dashboard
- Private key is encrypted and saved only on the Dashboard
Request Signing and Verification
OpenSSL signs requests using SHA-256 by default.
The child site only processes requests with valid signatures that match its stored public key.
HTTPS Encryption and Certificate Verification
HTTPS encrypts request and response contents in transit. Request signing authenticates requests but does not encrypt an HTTP connection, so use HTTPS URLs for connected child sites. SSL certificate verification is enabled by default. You can configure it globally or per site. Keep it enabled to verify the child site’s certificate.HTTPS Request Structure
MainWP Dashboard sends requests to each child site’s configured URL using cURL. The following example uses HTTPS. Requests include:Example Sync Request
mainwpsignature doesn’t match, the child site rejects the request.
Request Parameter Escaping
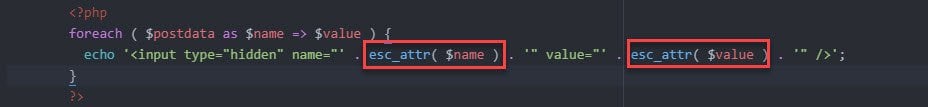
Before sending any request to a child site, MainWP Dashboard escapes all parameter values to prevent code injection. For example, the Jump to WP Admin feature escapesname and value attributes using esc_attr():
Why This Matters
This escaping protects against scenarios where an attacker might:- Trick you into clicking a crafted link
- Attempt to pass malicious code through request parameters
Complete Request Flow
The security system works as follows:- Preparation: Dashboard escapes all request attributes
- Transmission: HTTPS request sent with MainWP Signature and parameters
- Verification: Child site validates signature against stored public key
- Execution: Only authenticated requests are processed
Related Resources
- MainWP Security - Security overview
- OpenSSL Key Encryption - Private key encryption
- API Key Storage - Credential encryption
- Two-Factor Authentication - Additional login security